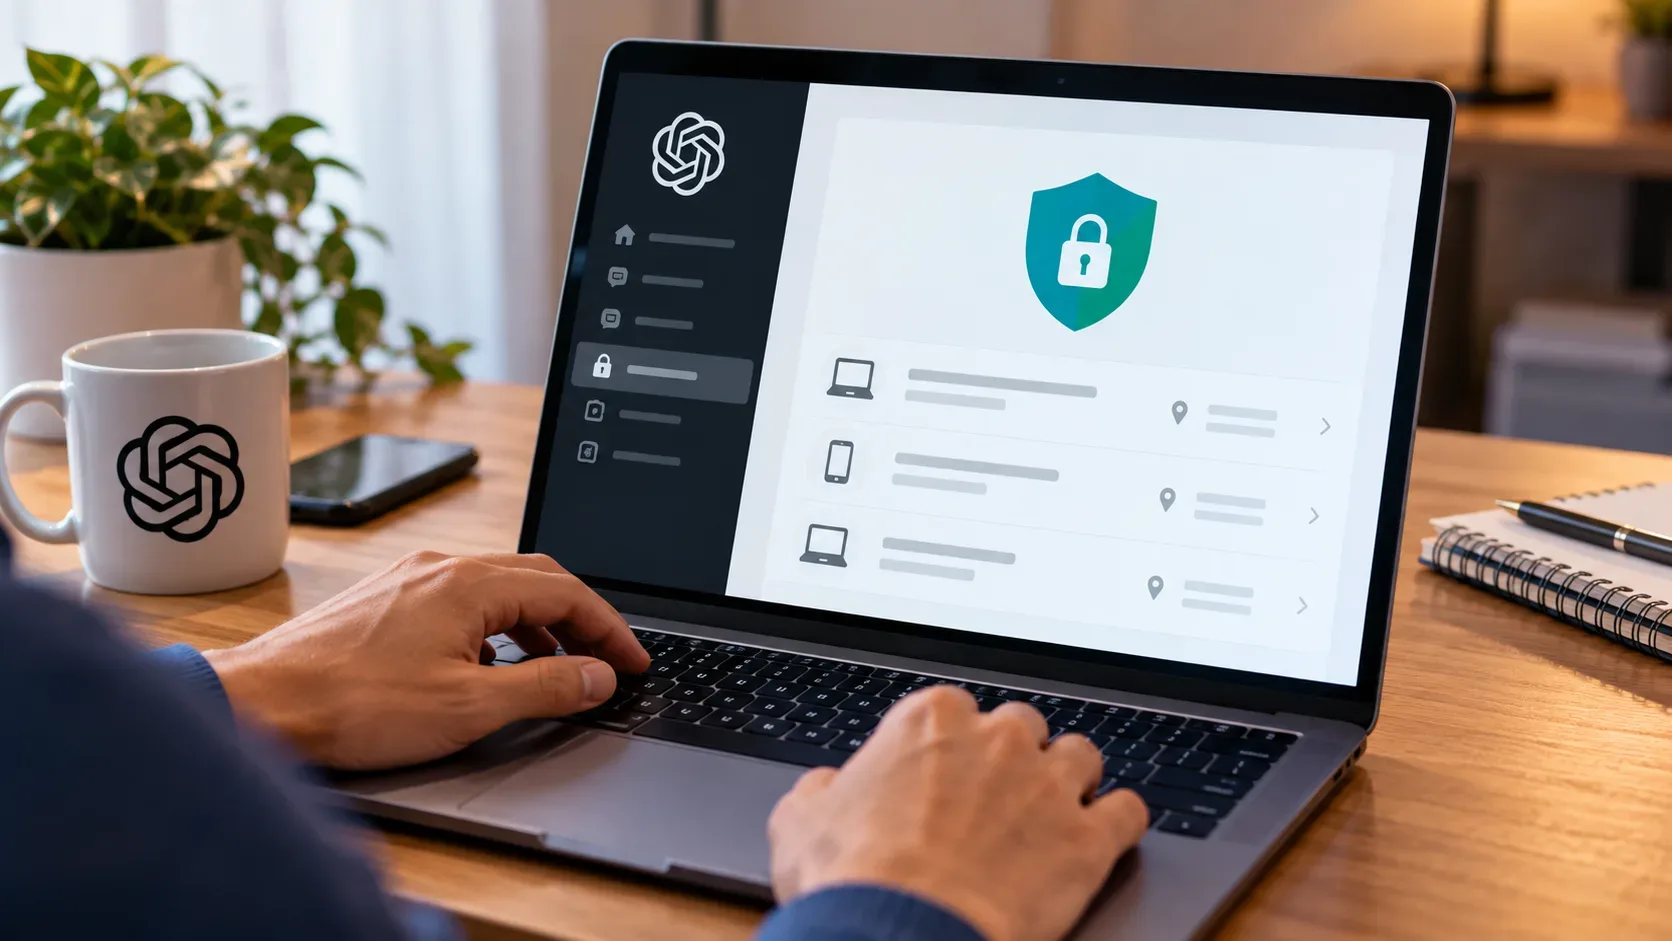
ChatGPT now offers a Security history view for reviewing recent security activity on an OpenAI account. According to OpenAI, the feature was announced on September 25, 2026 and, on ChatGPT web, is available at Settings > Security and login > Security history. The history includes events such as sign-ins, sign-outs, password changes, changes to multi-factor authentication (MFA), passkeys, and other security settings.
Where to find ChatGPT security history
- Open ChatGPT on the web and sign in to your account.
- Open Settings.
- Select Security and login.
- Open Security history.
This is the path documented by OpenAI for reviewing the feature in a browser. The official documentation describes the history as a view of recent security events, but the materials consulted do not specify a fixed retention period or a set number of days of visible records.
What appears in each record
Events can include the activity type, time, location, and device details. OpenAI notes that some information may be approximate or unavailable, so a single detail should not automatically be treated as proof that an account was compromised.
| Event type | What the history helps you check | How to interpret it |
|---|---|---|
| Sign-in | When a login occurred and, when available, the associated location and device. | Compare the time and device with your own activity. Location and device details may be approximate. |
| Sign-out | Logout records associated with recent account activity. | These help reconstruct the sequence of access when reviewed alongside sign-in events. |
| Password change | Changes related to the account password. | If you use a password and do not recognize the change, treat it as a reason to secure the account immediately. |
| MFA | Changes to multi-factor authentication. | Check whether enabling, removing, or changing a method matches an action you performed. |
| Passkeys | Changes involving passkeys linked to the account. | An unfamiliar change is a reason to review your sign-in methods and active sessions. |
| Other security settings | Additional changes that OpenAI records as security events. | Use the event time and available details to compare the record with your own activity. |
Security history and active sessions are different
Security history is used to review past events. Active sessions is the area for reviewing and managing sessions that are currently active. On ChatGPT web, OpenAI directs users to Settings > Security and login > Active sessions. From there, you can log out of all account sessions.
This distinction matters: seeing an older sign-in in the history does not, by itself, mean that session is still open. To check which access is still active and end connections, use the active sessions area.
What to do if you see access you do not recognize
OpenAI recommends securing credentials and sessions rather than relying only on enabling MFA. The reason is that enabling MFA does not automatically terminate sessions that were already active.
- If you use a password and believe it was exposed, change it immediately. Use a strong, unique password for the account.
- Log out of all active sessions. On ChatGPT web, go to Settings > Security and login > Active sessions and choose the option to log out of all sessions. OpenAI says other ChatGPT sessions may take up to 30 minutes to be logged out.
- Review MFA, passkeys, and other security options. Confirm that the registered methods belong to you. Enable MFA if you are not already using it, while remembering that MFA does not replace ending sessions that are already open.
- Review security history again. Record or preserve details of activity you did not perform because that information may help with account recovery.
- If you use the OpenAI API, review API keys too. OpenAI advises deleting potentially exposed keys and reviewing usage for unexpected activity.
- Contact OpenAI Support if you suspect compromise. Support can be reached by opening a new chat on the Help Center and providing details about activity you did not authorize.
How to review the history without overreacting
Use the history as a verification trail. First, check whether the event time matches something you did. Then review device and location information, keeping in mind that OpenAI says those details can be approximate or unavailable. Next, compare the event with security changes you recently made, such as enabling an MFA method or adding a passkey.
If the activity still does not match, move to the account-protection steps. Security history helps identify and organize the facts, but responding to a possible unauthorized access event depends on securing credentials, ending sessions, and reviewing authentication methods.